Translated with AI from the Russian original.

"SMEs are becoming easy prey for inexperienced hackers due to the lower barrier to entry into cybercrime and the development of automated technologies such as AI," notes Anatoly Peskovsky, expert at the IZ:SOC Cyberattack Monitoring and Counteraction Center of Informzashchita.
According to Informzashchita, 37% of small and medium-sized enterprises (SMEs) consider their level of information security (IS) to be insufficient. Since 2022, the number of such companies has increased by 32%. The reason is the growing number of cybercriminals who are increasingly choosing small companies as targets.

At the same time, large companies, thanks to significant investments in information security, are half as likely to face threats than a year ago. Experts emphasize the need for SMEs to use outsourcing and service SOCs to increase the level of security and optimize costs.
Now on the front page

Articles

Why even a PC case should be branded

In Russian conditions, the popularity of PCs assembled by small local companies or in-house corporate IT departments continues to grow rapidly. Such solutions have historically been more popular in Russia than in other developed markets, but today new nuances have emerged in the segment's evolution, which we discussed with Karim LASKRI, Business Director of FSP Group in the CIS region.

News

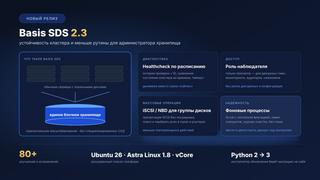
Storage you can trust in the background: Basis SDS 2.3 released with scheduled diagnostics and an observer role

A storage system is the only infrastructure layer where an error cannot be “rolled back”: neither a reboot nor a configuration rollback will restore lost data. That is why users expect predictability from software-defined storage rather than just new features—ensuring background processes finish what they started, and administrators can see the cluster status not only “right now,” but also over time.