Aladdin has introduced Aladdin LiveTSM, a trusted boot tool for workstations, servers, and specialized equipment based on x86-64 processors with UEFI support. The solution is designed to protect against operating system bootloader and kernel tampering. It has received FSTEC of Russia certificate No. 5124 under trust level 4 (UD4).
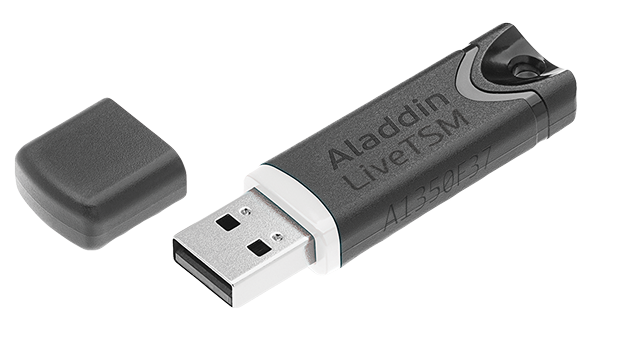
Aladdin LiveTSM verifies component integrity before OS startup using UEFI Secure Boot. The system monitors its own state, the user, hardware configuration, and authorized boot objects. If the check detects a violation of the defined policy, startup is blocked, and event information is logged. The solution does not require modifying hardware firmware to operate.
The device supports Windows 10 and 11, as well as Linux distributions Astra Linux 1.8, RED OS 8, “Alt 8 SP”, and “ROSA Khrom”. Direct kernel verification and booting via the standard bootloader are supported for Linux.
The lineup includes three USB models: TSMX-T110 for servers and specialized equipment, TSMX-E110 for desktop PCs with user authentication, and the external TSMX-C110 for laptops and mobile workstations. The modules can be installed inside the chassis or connected to an external USB port.
The solution is designed, among other applications, for use in government information systems, industrial control systems, and significant critical information infrastructure facilities. Moving forward, Aladdin plans to expand the list of compatible operating systems and hardware platforms.